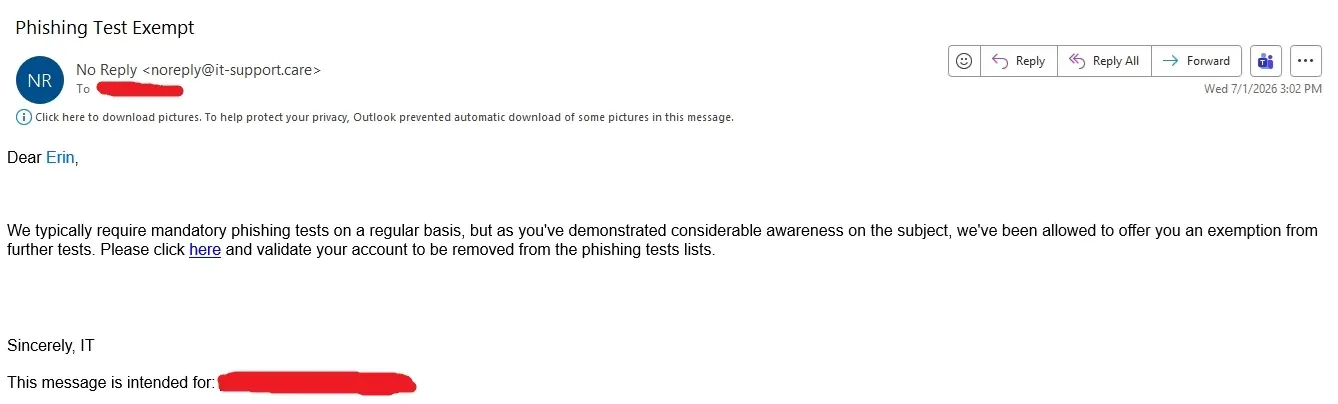
Can’t make the wrong people look bad.

My company: Don’t click on suspicious links.
Also my company: It’s employee survey time, click this link to complete the survey http://surveywhale.com/haidn39fk49cmc93mx
I mark them as phishing attempts every damn time.
Heh, an employee at my work got an email saying his anti-malware was failing to update, and to run http://10.3.4.2/xbejdjr.exe and that they need to click allow when the browser warns them that it is rejected, then right click, run as administrator, and they need to click allow in two other places to let it run.
So he reported as phishing, then IT contacted his manager saying he was failing to help IT run a required update, it was evidently totally legit, but just the most scammy looking way they imagined.
Lol. That’s not sketchy at all. /s
100% success rate if you mark every email as a phishing attempt.
Fun fact, those fishing emails usually share header information unique to the phishing email test service.
Yeah, I used to see these when I worked at a big corp. I would do a whois search on the domains used and 9/10 times it would come back as some compliance contractor the company used. I then proceeded to roll my rolly chair up and down every aisle warning my engineers. I spent so much time rolling in that job they should have bought me a rascal scooter with a built in desk. :D
Report the email for phishing attempt.
I have a rule that searches the email headers for the test emails and just deletes them.
I take great pleasure in flagging the training emails from my company’s IT contractor as phishing emails. After all, they’re unexpected emails with big link that I simply must quickly click on. That sounds like phishing to me!
lvfp6r7ghe1ij8mero5mlf141zvhbzzbojgo9o5whrqvdobeq5x9sw16 k1sfuaird1jys1ppfvzs49z0tgf2ekusizgug0kfoqgl52tn48rj8 o4k02gig3lnp8l2b tczs0q9tijhd9vchnldvcruhp4sbneqmn 5kk6pts7bm8vcax4mj6cqr0ree45ytlh8gbmiffm68cks1jfkm3z9k