Now that I have time for hobbies again I wanna dive right in to building up a home lab. Right now I just have a Netgear router that reached end of life, and a NAS i’d like to make accessible remotely, and a DIY router seems like the correct next step for me. I’m very interested in ad-blocking network wide and someday I’d like to host my own little webpage, but for now I’m really just barely getting started.
I’m information gathering, I don’t know what I don’t know and my networking skills are pretty weak anyway. But even if your needs and desires have nothing to do with mine, I also just like to hear people talk about their set ups. Please? 🌞
You must log in or register to comment.
I bought a firewall appliance based on an Intel CPU, with 4x 2.5gbps Ethernet ports, 8gb ram. Installed opnSense on it and been super happy even since!
A bit pricey the hardware, but it’s been totally rock solid for almost two years now.
I have configured unbound with ad blocking on opnSense, and it has every single option I would ever want on it. Amazing stuff.
I’m eyeing a similar one, but with 2x sfp+ ports too.
I’ve seen a lot of people on YouTube talking about this or that cast off networking device that they turned into a router. I do find the idea of repurposing especially old tech appealing. Or did you buy it brand new?
I bought it new, but of course you can repurpose old hardware!
Opnsense on whatever. Plus pihole for DNS/adblock.
I put Opnsense on an Intel Pentium G3220 and it’s been rock solid for gigabit.
Not sure how “DIY” you want to go. I’ve been liking OPNSense though. Running it on an air cooled Protectli box.
Handles a symmetric 2Gbps connection just fine.
This is what I’m doing too. I’m super happy with the results and how many options are now open to me.
Originally I was thinking I’d find a used business mini pc and put some open source router OS on there, still haven’t picked which one. But I’ve gotten super into, like, being cautious about power consumption and some of the little boxes you can get on AliExpress seem like that might be a better option? I’m not sure yet. What’s a Protectli, if you don’t mind?
This is protectli: https://protectli.com/
If you’re especially looking for good power consumption, I’d look into some embedded system with OpenWRT. I was especially looking for something that could handle high bandwidth and manage some higher level features that OPNSense has.
Thank you!
Someone suggested seeing if I could install openWRT on my current router, I might start there instead of buying anything right away, I can always grow more later as I find I’m ready to start doing x, y. or z if I find I need to.
But I’d never heard of protectli. I have a feeling that, since I was just browsing youtube to start, I mostly only learned about companies that are doing youtube sponsorships lol
Someone suggested seeing if I could install openWRT on my current router, I might start there instead of buying anything right away, I can always grow more later as I find I’m ready to start doing x, y. or z if I find I need to.
I like the spirit! That’s an excellent place to start. If you find you need more later, there’s plenty of options to grow.
OpenWRT all the way.
Skynet firewall
PiHole
Stable IP addresses and a private interface for family phones/laptops/pcs
Guest network for nasty Roku TV/peleton
EDIT: my favorite thing about Skynet is the new-ish ability to filter by country
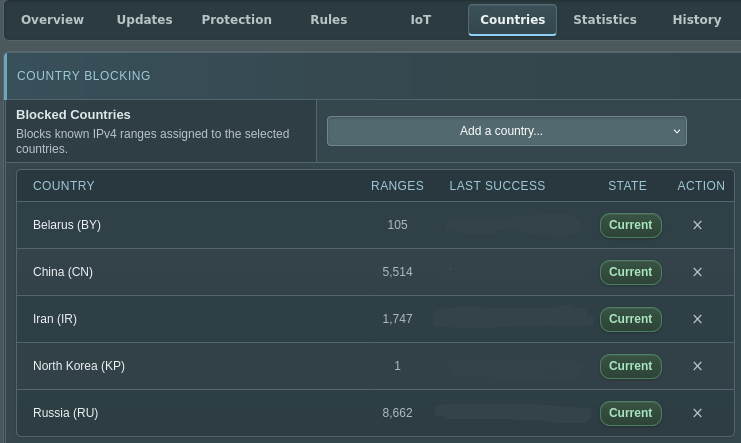
I never even thought about a guest network for different services. Why do you do that, if you don’t mind? Privacy?
You could configure different settings, such as preventing the device from connecting to ad servers. You also prevent it from scanning your network to learn about all your devices, since all it would be limited to that isolated network.
Does peloton do that!? 🥲
I don’t know. Is it internet connected? If so I wouldn’t trust it…
Many home grade routers allow you to set up a guest WiFi network though so you may be able to isolate it that way if you’re concerned/can determine what telemetry it’s sending from the privacy policy or other reports.
This article talks about their website’s standard creepy tracking cookies and stuff, which depressingly everyone does. https://blog.avast.com/what-peloton-knows-about-you-avast
But if it has Bluetooth and WiFi it has a lot of potential for tracking all sorts of things. I don’t have one and don’t know if they’re using that potential, but it’s there. It would be interesting to investigate.
I only got into privacy stuff like a year ago, but I was really focused on thinking about my phone and not as much my home network (unless we’re talking like, cloud services that are also accessed on desktop, I was already worried about those). That’s a spooky but totally valid thought imo. Agree, would be a good new rabbit hole to explore.
It’s a big rabbit hole for sure, with how many household devices are internet connected and the concerning capabilities they offer. And an expensive one if you seek to replace devices at home.
Guest Network in OpenWRT prevents inter-device communication on the LAN. So the thing can talk to its cloud service or whatever but can’t see my phone/laptop/PCs.
This means that untrusted devices which get pw0ned (or are surveillance-by-design) can’t then get into your more important machines. Most people use guest networks for IoT devices like Ring cams and smart washing machines but I don’t even own shit like that.
Lol I also passed up on ring cameras, i’d like to have a camera someday but I don’t want to go through Amazon.
I wonder if I should set up a guest network for my mother-in-law. 🤔 My husband is very on-board with my privacy-focused desires and cautious about what we invite into the home but my MIL, well, is old.
I usually just use proper network devices. OpenWRT will generally run on anything with Mediatec or Qualcomm based assuming it has support
Another vote for openwrt
When I retire my desktop PC, the old parts become my router. If you have two network ports, it can do it.
To warrant the power bill, it’s also a NAS, NVR, mail server, print server and web server.
All my Wifi APs are various home routers flashed with OpenWRT.
Running an email server sounds super super difficult
I’ve been running mine for over 20 years. It’s certainly got more difficult, especially to be able to reliably communicate with Gmail-hosted servers and outlook.com addresses, but SPF, DMARC, and DKIM are all pretty straightforward to set up. Tightening the encryption/hash algorithms you accept and “anonymizing” your server greetings takes some finesse as well, but I definitely prefer it this way.
I avoid the entire webmail and spam filtering aspects, smtp(s) and imap(s) only.
Not difficult with amazing software like mailcow
Oh, you can tear it down as soon as you get the certification.
Mine still runs decades later though.
I had a virtualized PFsense box for a while doing my inherent. Was actually pretty solid even when having to wrangle the quirks having a virtualized firewall/router caused.
I have something similar it’s been working great.
I have been thinking of trying to set up a “router on a stick” as a live backup but once I started researching it, it got daunting.
I do this at work. If you don’t do pass through for the NICs I’d highly suggest it. When it’s a router it’s insane how much the overhead can be.
We have a 4 gig connection and with the virtual nics got maybe just over 1gbit on a Xeon silver based R640. But after pass through solid 3.5ish. Not sure where the bottleneck is currently, but our other servers do >4 just fine.
OpenWrt on Raspberry Pi 4 with UE300 dongle for the WAN side. 7 years of trouble-free operation so far.
What’s the throughput on that bad boi?
I’ve only tested up to 1Gb. It does 1Gb no probs, with SQM (QoS) which burns a lot of CPU.
Okay cool, thank you
I was using an N100 based mini PC and it did fine at 1gbit. But now that I have 3, and it’s realistically closer to 4 or 5 it doesn’t cut the mustard.
Proper hardware based routers are also just so much more efficient. That N100 machine was constantly hot to the touch. My new UniFi router uses less power and does 10 gig easily.
Can I ask what the 10 gig is for?
Gotta go fast. My WiFi can achieve > 1gbit, my internal network is already 10 gig. Why not support faster everywhere?
Sometimes it’s really that simple 🥰
I have 2.5G N100 and it works wonderfully at that rate. I think higher might be tough, but it still pushes that throughput even with IPS enabled in OPNsense.
The complained about heat is right though. I stuck a noctua fan on the top and it’s been happy since. It lives my closet, so noise isn’t a facto anyways
i had a cheap made in china consumer router with mt7621 on it, porting openwrt was surprisingly easy and its been running well enough for the past 5 years. adguard home runs on it and handles dns adblocking
someone else suggested openwrt on my current EOL router, i might just try that! like, i think eventually I might still want something more robust, but it sounds like a pretty good starting point
even cheap consumer router these days are actually surprisingly capable. mine’s from 2015! what model do you have? might be hard if it’s a realtek/brcm chipset… mediatek(ralink) and qualcomm(atheros) are mostly well supported
Apparently it’s older than I thought and not supported! I could use another project called dd-wrt though
I got a spiffy little fanless micro PC with five Ethernet ports, installed Ubuntu, and wrote my own iptables rules and installed pihole.
Now THAT is diy
Does it run cool enough?
Yeah, it’s barely doing anything except shifting packets and doing DNS. Load is around 0.08 on a four core processor.
I have a Flint 2 with OpenWRT installed, it handles all my home networking. I have a handful of vLANs and I think the count is still 5 APs. I am currently considering adding a 6th for HA to TV vLAN, one that cannot access the WAN just HA. People have disagreements over OpenWRT and pfsense, or opensense not sure which is the “FOSS” version, but OpenWRT is not going to try and upsell you.
I am sure OpenWRT offers some ad blocking but I already had two finally tuned piholes. There are arguments between pihole and adguard home. I started with pihole I have tried adguard but went back to pihole.
Can I ask why you didn’t like adguard as much? :o
That was years ago so I do not remember. Maybe it was that I was just used to pihole? If I tried now I think the answer would be the same, but it would be because I have a finally curated list and regex.
Lol so real. Thank you.
Got a “Dell Wyze 5070 extended”, the extended is important because it lets it have a half height PCIe card. Put a dual NIC Intel card in it. It came with 8 GB of RAM and a 64 GB SATA M.2 drive, plenty. Price out a power brick if it doesn’t come with one, which is a Dell laptop one; it refuses to turn on with a PCIe card in and if the power brick is less than 130W (DA130PE1-00 is a product # of it)!! Very annoying. Note the Intel atom processor in it lacks AVX2 instructions which makes mongoDB past v4 not work on it, so you can’t run the Unifi controller, which has vexed me. But it’s fine for internet routing! Never tested throughput but others have online.
(Note: I would not do this now!) I put proxmox on it then did opnsense (passing through the PCIe NICs) and Debian. I chose opnsense over openwrt because opnsense had an automatic update functionality, while openwrt required you to manually wipe the OS and reinstall - when they fix nasty upgrade path that I’ll come knockin. (Openwrt is like that because that’s how routers do upgrades)
I would not choose proxmox now because its upgrade path is fraught since the free level is rolling and they’ve had critical breaking update errors in the past. No good for your router setup. I want upgrades on and automatic so I don’t get kiddie script hacked.
I’m prepping to do either opnsense only and not in a VM or Debian with Incus (VM manager like promox, but not its own OS) installed and then opnsense in a VM. I’m leaning opnsense direct to just make sure my router works, but I’ve never had trouble with Debian yet so still pondering.
I run a pihole and wireguard on the current Debian VM, and opnsense can do wireguard so most of the way there. In the future I’ll switch that pihole instance (wherever it is) to adguardhome, the local rewrite rules in pihole don’t support wildcards so it’s annoying af to have to load in every local domain I set up.
This has worked well for years and I’ve never measured power but I presume it is low.
Hope this infodump helps!
It really did, thank you :) No one else mentioned updating as far as I know, and that wasn’t something I really thought about at all, coming from a commercial router. Plus I just enjoyed your journey. I think I’ll need wireguard to safely access my NAS remotely so that’s good to know too.
Feel free to ask any Qs if any come up, there is ?likely? better value than the Wyze 5070 extended now a days, I looked and bozos still want like $100 for it. Getting AVX2 would be a solid W for software in the future and worth a minor increase in cost. An ARM board (as long as it has UEFI and can boot regular Debian - not a custom distro for the board) would be a solid move too, but you’ll not get Opnsense then - it’s openwrt only for ARM.
This of course is me thinking of pricing when it wasn’t AI bro “lemme order all your RAM on an IOU” stupid, good luck there!! Just opnsense does not need much RAM - like 3 GB is easily safe (mine is given 2GB right now; uses 600 MB right now but I’ve seen it go past 1.5 GB sometimes). Straight Debian will add a gig or so. So even 4 GB would be fine. Proxmox is needy so it’s not fine there, but cutting it out of the equation would make 4 work if you want to save. And you’d prob get away with a $5 16 GB optane M.2 drive from China (aliexpress) with just opnsense - it’s using 3.2 GB of the 16 I’ve given it. And the Optane drive will never wear out as a bonus.
Edit: I’d estimate stock Debian at ~6 GB used. I think both can fit in 16 GB, even with Debian loaded with Incus to run the Opnsense in a VM.
OPNsense on used dell optiplex. Very easy but it can do whatever you want to grow into as you learn more.
dell optiplex
How many NICs can you cram in these? I added a second one to my Lenovo Tinys but some more are nice for a FW…
Two NIC. I’m usually using the SFF. I went 10G last year and it’s been so great. Single, used, low profile, dual port SFP+ module. One port has SFP+ to RJ45 to my modem. Other port is SFP+ passive DAC to a used Brocade ICX 2750.
This is what I did before I went to all unifi gear.
I was Unifi gear and then went back to Opnsense :P. That shit is way too expensive to replace.
The extended warranty is pretty damn good, but that’s expensive too lol
Is the power consumption too bad, if you know?
It’s currently a N100 mini-pc running Debian, but in the past it’s been all kinds of random hardware including a busted old laptop with an expresscard-PCIe riser for the second NIC. Anything can be a router if you know what you’re doing!
thank you, this is a great post! I like your blog!
Thanks!